

What We Build
TAK Devs’ software audit services cover eight areas of risk. Every engagement is scoped to the ones that matter for your system, not sold as an all-or-nothing package.
Code That’s Quietly Rotting
Find the tech debt before it doubles your dev costs
We review architecture, code quality, and technical debt across your codebase, human-written and AI-generated alike, then hand you a prioritized fix list instead of a vague “needs work” verdict.
- Full codebase review scored against industry benchmarks for maintainability, reusability, and extensibility
- Architecture assessment that shows where a refactor pays for itself, and where it doesn’t
- Side-by-side comparison of human-written and AI-generated code quality, since they don’t degrade the same way
- A prioritized refactor roadmap, ranked by risk and effort, not a 40-page report nobody reads
- Frontend and backend reviewed separately so styling debt and logic debt don’t get lumped together
Security Gaps, Found Early
SAST, penetration testing, and secure design review in one pass
We combine automated scanning, manual penetration testing, and a secure design review to catch what a scanner alone misses, then map every finding to your compliance targets.
- Static Application Security Testing (SAST) covering OWASP Top 10 vulnerabilities in application and API code
- Penetration testing that simulates real attacks against authentication, authorization, and business logic, not just the login form
- Secure design review of password storage, identity and access management, and cryptography against industry best practice
- Findings mapped to ISO 27001 and GDPR requirements where relevant, so compliance gaps surface alongside technical ones
- Delivered under TAK Devs’ own ISO 27001-certified security practice, not a subcontracted checklist
Cloud And Infrastructure Audits
CI/CD and cloud configuration, checked before they break at scale
We review your CI/CD pipeline, containerization, and cloud architecture to find the configuration drift and inefficiencies that turn into 3am incidents.
- Pipeline review that flags manual steps, flaky tests, and deployment bottlenecks slowing your release cadence
- Cloud architecture assessment across AWS, Google Cloud, or Microsoft Azure, covering cost, resilience, and security posture
- Containerization and infrastructure-as-code review checked against hardening standards, not just “does it run”
- Targets the kind of configuration issues behind TAK Devs’ typical 20-35% cloud cost reduction on infrastructure audits
- Storage and backup review covering data quality, capacity planning, and disaster recovery readiness
Test Coverage That Lies
Find the gaps your test suite isn't telling you about
We assess your automated and manual testing processes, tools, and coverage to show exactly where bugs are slipping through to production.
- Coverage analysis across unit, integration, and end-to-end tests, mapped against your actual production incident history
- Review of test tooling and CI integration to catch flaky or skipped tests hiding behind a green pipeline
- A balanced automation and manual testing plan, since neither one alone catches everything
- Cross-platform compatibility checks across the devices, operating systems, and browsers your users actually run
- Process review of how bugs get triaged, reproduced, and closed, not just how many tickets exist
UX That’s Costing Conversions
Find why users bounce before they convert
We review your product’s usability and interface consistency to find the friction points quietly costing you retention and conversions.
- Heuristic review of core user flows, flagging friction points before they show up in churn data
- Consistency check across product interfaces so the experience doesn’t fracture between screens or platforms
- Accessibility review against WCAG guidelines, since usability and compliance overlap more than most teams realize
- Root-cause analysis of low-engagement screens, not just a redesign wish list
AI Models, Actually Checked
Know if your model is production-ready or just demo-ready
We review AI and ML models for accuracy, efficiency, and security risk, and audit AI-generated code the same way we audit human-written code, because it doesn’t get a pass just because a model wrote it.
- Model performance and drift review to confirm the system still works the way it did on day one
- Security review of AI infrastructure (MLOps), including data pipelines and model access controls
- Line-by-line review of AI-generated code for the vulnerabilities and shortcuts automated tools tend to leave behind
- Recommendations for closing the gap between a notebook that works and a model that ships
Open Source, Fully Mapped
Undisclosed dependencies can derail a deal or a deploy
We map the open source and third-party components in your codebase to flag license conflicts and unpatched vulnerabilities before they become someone else’s problem.
- Full inventory of open source and third-party components in use, with license obligations flagged clearly
- Known-vulnerability check against current advisories, not a snapshot from whenever the last audit happened
- Especially relevant ahead of a fundraise, acquisition, or enterprise sales deal where due diligence gets real
Process Debt, Named
Fix the process before you fix the same bug again
We assess the practices behind your software development lifecycle, including how AI tools get used, to find where process gaps are quietly generating the bugs you keep fixing.
- Review of coding standards, code review practices, and tooling against what actually reduces defects
- Assessment of how AI coding assistants are used on your team, and where guardrails are missing
- Onboarding and documentation review, since a lot of “bugs” are really tribal knowledge nobody wrote down
- A roadmap for reducing development and maintenance costs, not just a list of what’s wrong
Trusted and recognized across the industry


How TAK Devs Works
Process diagrams look the same at every agency. What matters is what actually happens inside each phase. Here is how we work in practice, refined across 150+ delivered projects.
- 150+ projects delivered
- ISO 9001 quality certified
- ISO 27001 security certified
Discovery Call
We uncover what you actually need first.
Output: problem briefScoping Workshop
Goals become a costed, prioritised delivery plan.
Output: scope and roadmapSprint Delivery
Tested, working software shipped every sprint.
Output: working softwareLaunch & Handoff
Live deployment, full docs, clean knowledge transfer.
Output: live product and docsOngoing Support
We monitor, maintain, and scale after launch.
Output: monitored and maintainedNot sure which phase you are in? Start with a discovery call and we will tell you honestly.
Book a discovery callStruggling to keep up with development demands?
See how we can streamline your workflow.
No commitment required | Takes 20 minutes !
Who We Work With
If any of these hits close to home, you are in the right place.
Founders
CTOs and VPs of Engineering
Ops Leaders
Data and ML Leads
Product Managers
Industries We Serve
Domain-specific risk that a generic audit checklist would miss.
Health Tech
Compliance-heavy audits for HIPAA-aligned platforms and patient data systems.
Fintech
Security and compliance reviews for systems handling financial data and transactions.
SaaS
Architecture and infrastructure audits for platforms scaling past their original design.
Legal Technology
Security and process audits for systems handling privileged, sensitive documents.
Retail and E-commerce
Performance and infrastructure audits ahead of peak-traffic seasons.
Travel and Hospitality
Cross-platform and integration audits across booking and marketplace systems.
Automotive and Mobility
Code quality and AI model audits for connected vehicle and mobility systems.
Consulting Providers
Audits that give consulting firms an independent technical opinion to hand their own clients.
Why Teams Pick TAK DEVs
Fixed-Price Scoping
Transparent, fixed-price audit engagements. No surprise invoices, no scope creep billed by the hour.
Senior Engineers Only
100% of every audit team is senior, vetted engineers, not junior staff hidden behind a partner’s logo.
ISO-Certified Practice
TAK Devs is ISO 9001 and ISO 27001 certified, so the audit itself follows the same quality and security standards it is checking your code against.
Boutique Capacity
TAK Devs takes on a limited number of new engagements each quarter, so your audit gets senior attention, not overflow capacity.
Built It, Then Audited It
150+ projects delivered and systems built to handle 2M+ daily users, so the audit comes from engineers who have shipped at that scale, not just reviewed it.
Findings You Can Action
Every audit ends with a prioritized roadmap ranked by risk and effort, not a report that sits in a drive folder.
What Working With TAK Devs Actually Looks Like
In early 2025, UpliftCare came to us with a clear challenge and a tight window. They needed a complete, HIPAA-compliant telehealth marketplace connecting patients, verified therapists, and healthcare institutions. The deadline was three months, set by an investor presentation they could not move.
There was no technical architecture. No defined roadmap. Just a vision and a date.
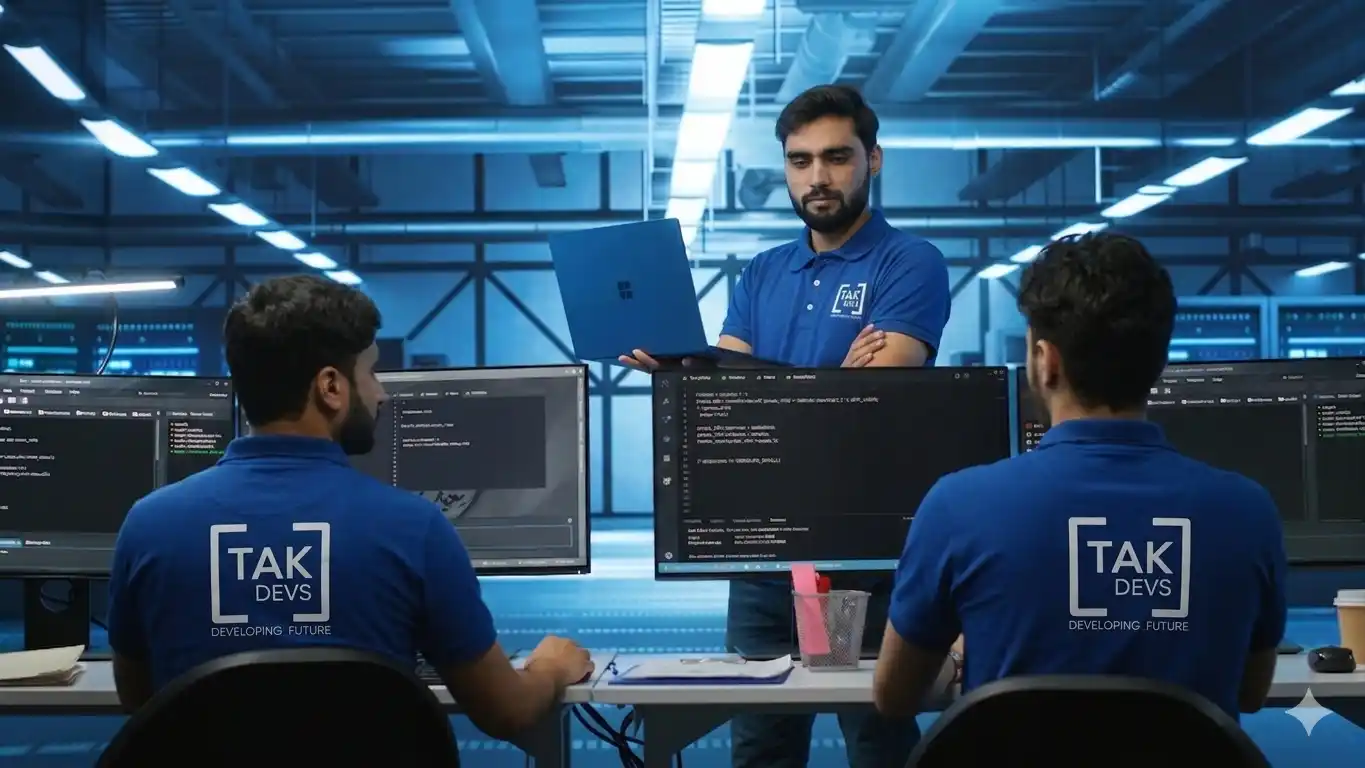
TAK Devs took on the full product lifecycle.
In six sprints and twelve weeks, we delivered:
Four connected portals covering Patient, Therapist, Admin, and Institutional workflows
Real-time video consultations via WebRTC, integrated Stripe payments, and smart scheduling
100% HIPAA-aligned architecture with full encryption across all data flows
Automated credential verification that reduced therapist onboarding time by 70%
CI/CD pipelines, automated testing, and AWS-based deployment ready for production from day one
Testimonials
I'm happy with TAK Devs Pvt Ltd's work quality. Our engagement with TAK Devs Pvt Ltd is a huge success. Our project is very complex and has many engineering metrics and variables, and the team delivers high-quality work.
TAK Devs Pvt Ltd delivered a robust system designed to handle 2 million daily users, achieving a seamless integration of PDF creation as part of the authentication process. The team consistently met deadlines and was highly responsive, flexible, transparent, understanding, and proactive.
Thanks to TAK Devs Pvt Ltd, the client can seamlessly track session duration, user engagement, and login metrics. They also can efficiently monitor appointment bookings, assess client-therapist match rates, and collect feedback. The service provider's knowledge and quality delivery are exemplary.
TAK Devs Pvt Ltd delivered a functional POC and offered detailed guidance throughout the development process. The team was helpful in explaining the project's complexities for the client to understand everything thoroughly. They communicated via virtual meetings, email, and messages.
Great communication, top understanding of Spec, autonomous development. Everything Perfect.
Real professionists, always ready to help our resident team. It's a pleasure to work with them.
Great work, implemented everything 100% as per our specifications, and very fast!
TAK Devs Pvt Ltd's efforts have been met with positive acclaim. The team is always available and communicative via virtual meetings and email. Their software development expertise and listening skills make them stand out.
Frequently Asked Questions
What is a software audit, and why would I need one?
A software audit is an independent review of your codebase, infrastructure, security, or processes that shows you exactly what state your software is really in, not what the last status update said. TAK Devs runs software audit services covering code quality, security, infrastructure, QA, and AI systems, each ending in a prioritized, actionable report.
- Common triggers: pre-fundraise or acquisition due diligence, a modernization decision, a security incident, or a new CTO who wants an honest baseline
- Works alongside your internal team, not instead of them
How do I know if a software audit is worth it for my team?
If you cannot confidently answer “what is our biggest technical risk right now,” an audit is worth it. It replaces guesswork and internal politics with an independent, evidence-based answer.
- Especially valuable before a major investment decision: a rebuild, a cloud migration, or a fundraising round
- A focused audit can validate the question in days, not months
What is the difference between a basic, detailed, and custom audit?
It is scope and depth. A focused audit samples code and interviews the team to spot major risks fast. A detailed audit reviews the majority of your codebase and processes. A custom engagement targets the exact systems and risks you care about most.
- Most teams start focused, then go deeper on the priority areas the results surface
- Scope gets fixed in the scoping workshop, before any work starts, so there is no surprise expansion
How long does a software audit take?
Most TAK Devs audits run two to six weeks depending on scope, with a scoping workshop upfront to set the exact timeline before work starts. A single-system focused audit can land in days; a full codebase and infrastructure review takes longer.
- Delivered in bi-weekly cycles with visible progress, not a single report that appears at the end
- Timeline is confirmed in writing during scoping, before the engagement starts
What happens if the audit finds something serious?
Findings are flagged and prioritized by risk as they are found, not held until the final report. Critical security or compliance issues get surfaced immediately so you can act before the audit even finishes.
- Every finding is ranked by risk and effort to fix, so you know what to tackle first
- TAK Devs can move straight into remediation work if you want the same team to fix what it found
Do you sign NDAs and data protection agreements?
Yes. TAK Devs signs NDAs as standard practice, and audit work follows the same ISO 27001-certified security practice used across every engagement. Your code and data are handled under documented, certified controls, not informal promises.
- ISO 27001 certification covers TAK Devs’ information security management system
- Data handling terms are agreed in writing before any code is reviewed
Can you audit AI-generated code, not just code my team wrote?
Yes. TAK Devs reviews AI-generated code with the same scrutiny as human-written code, because AI models tend to leave behind a different pattern of vulnerabilities and shortcuts, not fewer of them.
- Covers code generated by AI coding assistants, agentic coding tools, and AI-assisted refactors
- Reported separately from human-written findings so you can see where each source of risk sits
What does a software audit cost?
Pricing depends on scope, but every TAK Devs audit runs on a fixed-price basis agreed during scoping, so there are no surprise invoices for extra hours. Smaller, focused audits typically cost a fraction of the technical debt they uncover.
- Fixed-price options available; hourly billing is not the default
- The scoping workshop is free and comes with a defined price before you commit
Who owns the audit findings and report?
You do. The audit report, findings, and any code recommendations belong to your organization, delivered as a standalone document you can use with your own team, investors, or acquirers, regardless of whether TAK Devs handles the fixes.
- No obligation to use TAK Devs for remediation work after the audit
- Report is written to be understood by both engineering and non-technical stakeholders
What if we start and realize it is not the right fit?
TAK Devs takes on a limited number of new engagements each quarter specifically to avoid this. If the scoping workshop shows it is not the right fit, TAK Devs will say so and point you toward who is better suited.
- No commitment beyond the scoping workshop, which takes about 20 minutes to schedule
- Boutique capacity means the team scoping your audit is the team running it